Monday, May 22, 2024

OpenClaw AI Agent Deployment Guide Released for Cross-Border Hardware
by
Published
Views:
On April 28, 2026, China’s Cyberspace Administration and the Ministry of Industry and Information Technology jointly issued the Guidance on Risk Management for Generative AI Agents in Industrial Deployment, establishing the first regulatory framework clarifying legal responsibility boundaries for AI-powered quality inspection systems in cross-border hardware manufacturing — particularly relevant for SMT AOI equipment vendors, AI-enhanced AOI+SPI integrated system providers, and industrial AI solution integrators.
Event Overview
On April 28, 2026, the Cyberspace Administration of China (CAC) and the Ministry of Industry and Information Technology (MIIT) jointly released the Guidance on Risk Management for Generative AI Agents in Industrial Deployment. The document explicitly defines liability attribution for AI-based quality inspection systems in three core functions: defect classification, process correction, and quality traceability. It specifies that manufacturers may be exempted from batch-return liability arising from algorithmic misjudgment — provided the AI system holds ISO/IEC 42001 certification and maintains complete, auditable training data logs.
Industries Affected
SMT Equipment Manufacturers
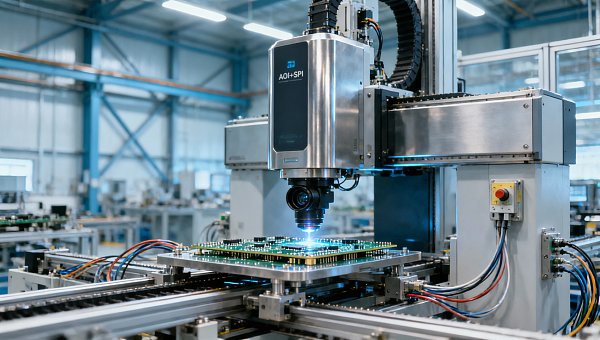
Manufacturers of automated optical inspection (AOI) and solder paste inspection (SPI) systems — especially those integrating generative AI for real-time defect analysis — are directly affected. The Guidance introduces a conditional liability shield, making compliance with ISO/IEC 42001 and rigorous log retention prerequisites for legal risk mitigation in overseas markets.
AI-Embedded Industrial Hardware Exporters
Exporters of AI-augmented SMT production line hardware (e.g., AOI+SPI co-deployed systems) face new pre-market requirements in key export destinations. The Guidance serves as a de facto reference standard for demonstrating AI governance maturity to foreign regulators and buyers, particularly in EU and ASEAN markets where AI accountability frameworks are evolving.
Industrial AI Solution Integrators
Firms embedding generative AI agents into factory-floor quality control workflows must now align technical implementation — including model versioning, input/output logging, and explainability mechanisms — with the Guidance’s operational accountability criteria. Their contractual obligations to end users may shift as liability boundaries become codified.
What Enterprises and Practitioners Should Focus On Now
Monitor official interpretation and supplementary implementation notices
The Guidance is a foundational policy document; sector-specific implementation rules, audit protocols for training data logs, and certification pathways under ISO/IEC 42001 for industrial AI agents remain pending. Stakeholders should track updates from CAC, MIIT, and the Standardization Administration of China (SAC).
Assess current AI system documentation against ISO/IEC 42001 Annex A controls
Manufacturers and integrators should conduct gap analyses focusing on Clause 8 (Data Governance), Clause 9 (System Lifecycle Management), and Clause 10 (Accountability & Human Oversight). Retrospective logging capability — especially for inference inputs and model decision rationales — is a critical readiness indicator.
Distinguish between regulatory signal and enforceable obligation
This Guidance sets risk management expectations but does not constitute binding legislation. Its immediate effect lies in shaping buyer due diligence, insurance underwriting terms, and contractual warranties — not in triggering penalties. Compliance remains voluntary unless referenced in procurement contracts or future mandatory standards.
Prepare technical documentation packages for international customers
For export-oriented firms, compiling ISO/IEC 42001 alignment statements, training data provenance summaries, and audit-ready log architecture diagrams will support commercial negotiations and reduce post-sale liability disputes in overseas deployments.
Editorial Perspective / Industry Observation
Observably, this Guidance functions primarily as a forward-looking policy signal — not an enforcement instrument. It reflects China’s intent to proactively align domestic AI governance with international industrial AI accountability trends, especially ahead of anticipated EU AI Act enforcement expansions in manufacturing sectors. Analysis shows the document prioritizes enabling export competitiveness over imposing prescriptive technical mandates. From an industry perspective, it more closely resembles a ‘compliance roadmap’ than a compliance deadline: its value lies in reducing ambiguity for exporters navigating fragmented global AI regulatory expectations, rather than introducing immediate legal constraints.
Conclusion
While not legally binding in isolation, the Guidance marks a structural step toward institutionalizing AI accountability in industrial hardware supply chains. It reframes AI quality inspection not solely as a performance specification, but as a governed process requiring demonstrable oversight infrastructure. For stakeholders, it is best understood as an early-stage alignment tool — one that clarifies *how* responsibility may be allocated in future disputes, rather than prescribing *who* bears absolute liability today.
Information Sources
Main source: Official release by the Cyberspace Administration of China (CAC) and Ministry of Industry and Information Technology (MIIT), dated April 28, 2026.
Note: Implementation details, certification procedures, and enforcement mechanisms remain under development and require ongoing observation.

The Archive Newsletter
Critical industrial intelligence delivered every Tuesday. Peer-reviewed summaries of the week's most impactful logistics and market shifts.