Monday, May 22, 2024

China’s 2026 Central Gov’t Civil Service Top-Up: 1,294 Posts, Boost for Domestic IT Hardware
by
Published
Views:
On May 8, 2026, China’s central government agencies and their affiliated institutions launched the 2026 civil service top-up recruitment, with 1,294 positions. The procurement demands tied to this recruitment—including trusted computing terminals, domestic servers, and security encryption modules—signal accelerated implementation of Phase II of the Government-Driven Information Technology Innovation (ITI) program. This development directly impacts industries involved in industrial-grade domestic substitution, including CNC systems, PLC hardware components, and ESG data acquisition terminals.
Event Overview
On May 8, 2026, central government organs and their direct subordinate institutions initiated the 2026 civil service top-up recruitment, planning to fill 1,294 posts. Publicly confirmed procurement requirements include information technology innovation (ITI)-compliant office terminals, domestically produced servers, and secure encryption modules. This action marks the full rollout of Phase II of the Party and government ITI initiative.
Industries Affected
Domestic Hardware Suppliers (Office & Server Tier)
These vendors supply trusted computing terminals and certified servers aligned with national standards. The top-up recruitment triggers immediate downstream procurement activity, as hiring agencies initiate equipment deployment ahead of onboarding new staff. Impact manifests in accelerated tendering cycles, tighter delivery timelines, and increased scrutiny on compliance with GB/T 22239 (Level 3 Cybersecurity Protection Standard) and GM/T 0002–2012 (SM4 encryption).
Industrial Automation Component Manufacturers
Suppliers of CNC control systems, programmable logic controllers (PLCs), and related hardware are indirectly affected. Analysis shows that the broader ITI Phase II rollout creates regulatory momentum: industrial equipment used in government-affiliated facilities—including research institutes and state-owned manufacturing units—is increasingly required to pass Level 3 cyber protection assessments and integrate SM4-based secure boot or data-at-rest encryption. Certification readiness now influences tender eligibility.
ESG Data Infrastructure Providers
Vendors offering environmental, social, and governance (ESG) data collection terminals—especially those deployed in public-sector monitoring networks—are impacted. From industry perspective, these devices face expanded compliance expectations: integration with national cryptographic infrastructure and alignment with newly emphasized data sovereignty protocols under the ITI framework. Certification pathways (e.g., SM4 support + Level 3 assessment) are becoming de facto entry requirements for public-sector tenders.
What Enterprises and Practitioners Should Monitor and Act On
Track official tender documents—not just policy announcements
Current procurement notices linked to the 1,294-post top-up list specific hardware models, certification versions (e.g., “SM4-compliant HSM module, version ≥2.1”), and delivery windows. Observably, actual tender language—not high-level policy statements—defines near-term technical and compliance obligations.
Verify certification status for priority product lines
For suppliers of CNC controllers, PLCs, and ESG terminals, current more relevant than broad roadmap planning is confirming whether existing SKUs already hold valid Level 3 assessment reports and SM4 algorithm validation certificates issued by authorized evaluation institutions. Unverified claims carry tender disqualification risk.
Distinguish between procurement-driven demand and long-term adoption signals
This top-up cycle reflects immediate staffing and infrastructure needs—not necessarily multi-year platform commitments. Analysis suggests it functions primarily as a catalyst for near-term certification acceleration and vendor qualification updates, rather than indicating wholesale replacement of legacy industrial systems across all agencies.
Prepare documentation packages for rapid response
Suppliers should pre-assemble standardized compliance dossiers: Level 3 assessment reports, SM4 implementation white papers, cryptographic module certification numbers, and test logs from accredited labs. These are now routinely requested within 5 working days of tender release.
Editorial Perspective / Industry Observation
This recruitment action is best understood not as a standalone hiring event, but as an operational milestone confirming Phase II ITI’s transition from planning to execution. Observably, it serves as a demand signal calibrated to real-world procurement timing—aligning hardware rollout with personnel onboarding schedules. It does not yet represent widespread system-level replacement across industrial sectors, but rather a targeted enforcement lever for certification compliance in frontline government IT and adjacent industrial infrastructure. Continued attention is warranted because subsequent agency-level tenders—especially those referencing ‘2026 top-up supporting infrastructure’—will likely replicate its technical and certification thresholds.
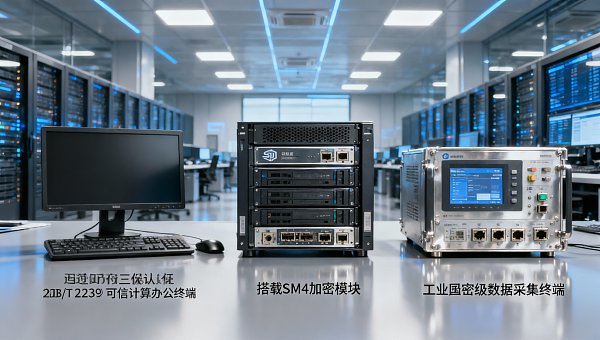
Conclusion: The 2026 central civil service top-up is a procedural trigger—not a market transformation event—but one that meaningfully compresses timelines for certification readiness and tender responsiveness among domestic hardware suppliers serving government and critical infrastructure segments. It is more accurately interpreted as a near-term compliance inflection point than a long-term demand shift.
Source: Official announcement by the State Administration for Public Affairs (SAPA), released May 8, 2026; publicly accessible tender notices issued under SAPA Procurement Notice No. 2026-ITI-05. Note: Certification timelines for CNC, PLC, and ESG terminal categories remain subject to ongoing evaluation by the National Cryptography Administration and Ministry of Public Security’s Cybersecurity Review Center—these aspects require continued observation.

The Archive Newsletter
Critical industrial intelligence delivered every Tuesday. Peer-reviewed summaries of the week's most impactful logistics and market shifts.